Posts

Showing posts with the label IOCs

Cyber Threat Intelligence for Autodidacts

Image
Introduction Cyber Threat Intelligence (CTI) analysts come from diverse backgrounds, and their roles can vary a lot depending on the type of organisation they work for. The path to becoming a CTI analyst can follow one of several routes, such as moving from Security Operations Center (SOC) and other information security roles, joining from university, or from law enforcement or military backgrounds. I’ve also met many who have radically changed trades and reskilled from jobs such as secondary school teachers to bar and hotel staff with great success. CTI teams can also vary significantly in their structure and focus. Some analysts work for vendors, providing intelligence to multiple clients across industries like, for example, Recorded Future’s Insikt Group. Others serve as defenders within a single company, working to protect that organization’s assets like, for example Equinix’s ETAC team. There are analysts who operate within government agencies as well, such as intelligence, se...
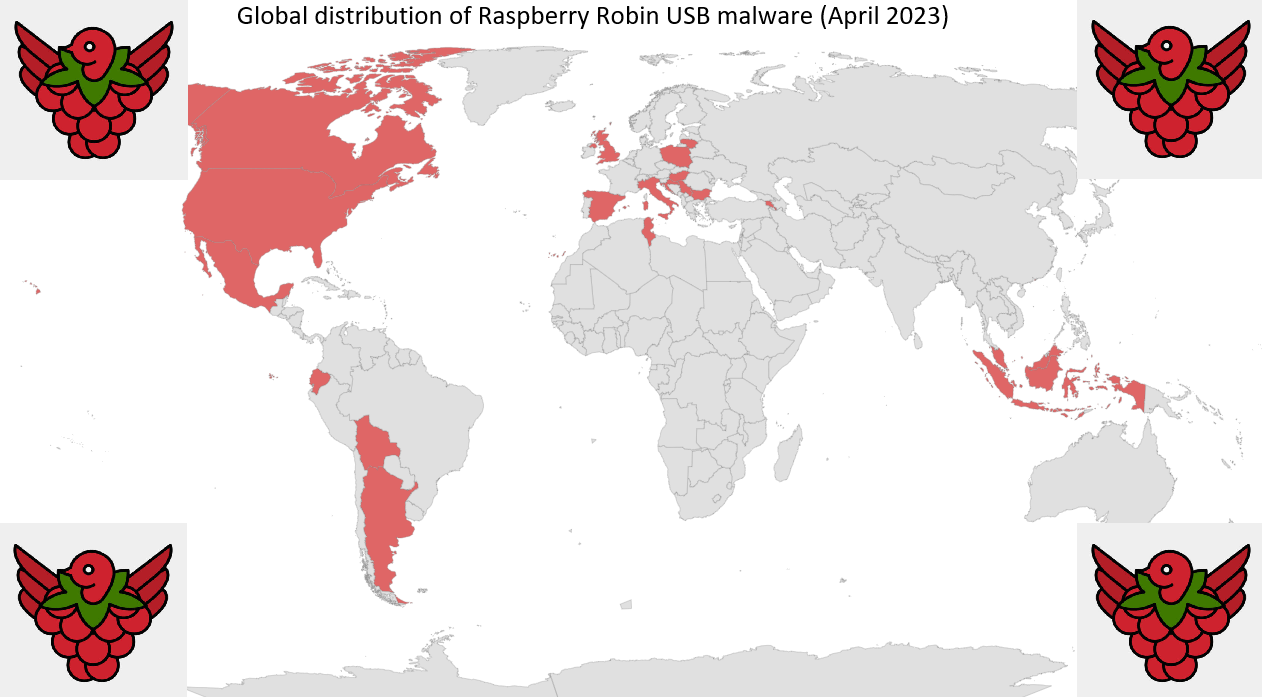
Raspberry Robin: A global USB malware campaign providing access to ransomware operators

Image
Logo credit: RedCanary Ever since it first appeared in late 2021, the Raspberry Robin malware campaign has been propagating globally. A number of threat intelligence reports by vendors such as RedCanary (who named it) and Microsoft (who track it as DEV-0856/Storm-0856) have covered the malware campaign in great detail.  In fact, the list of blogs I do recommend to read to catch up on this threat are as follows: https://redcanary.com/blog/raspberry-robin https://www.microsoft.com/en-us/security/blog/2022/10/27/raspberry-robin-worm-part-of-larger-ecosystem-facilitating-pre-ransomware-activity https://blog.sekoia.io/raspberry-robins-botnet-second-life/ https://decoded.avast.io/janvojtesek/raspberry-robins-roshtyak-a-little-lesson-in-trickery/ https://research.checkpoint.com/2023/raspberry-robin-anti-evasion-how-to-exploit-analysis/ https://securityintelligence.com/posts/raspberry-robin-worm-dridex-malware/ https://blogs.cisco.com/security/raspberry-robin-highly-evasive-worm-sprea...

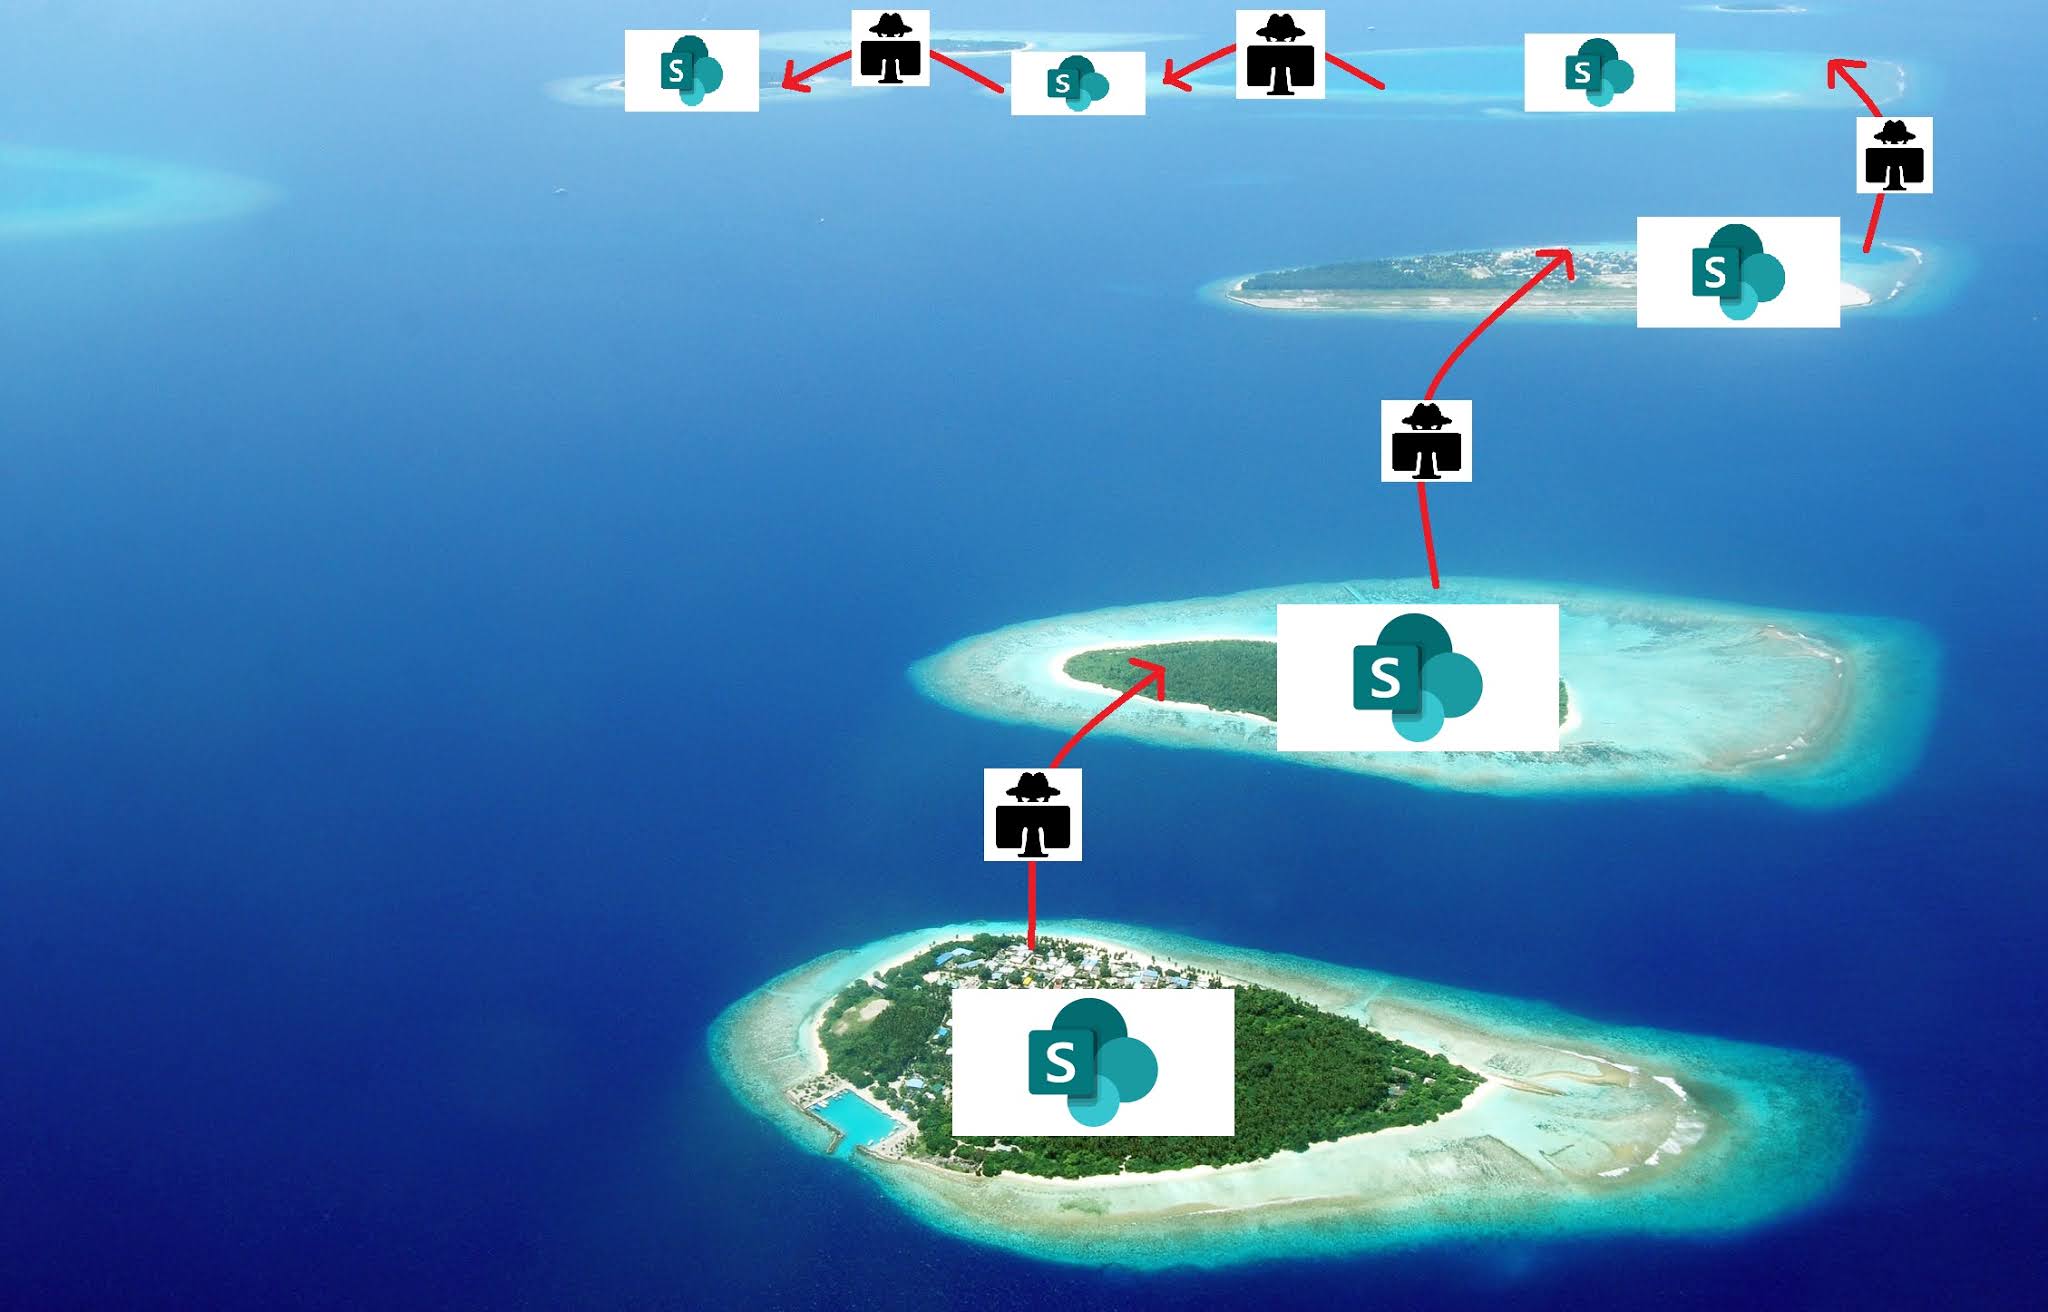
SharePoint Island Hopping: Phishing with compromised accounts

Image
  Phishing threat actors continue to launch successful credential harvesting campaigns via compromised Office 365 accounts. One of the most common themes for these campaigns is a "shared file" notification, whereby a compromised account shares a file with a user that is hosted in the SharePoint drive. The file is usually a PDF document that contains a URL to an external site embedded in an "open document" or "view file" button. If the user clicks on it and enters their credentials they are redirected to login.microsoftonline.com. Although this is an older scam, that has been around for several years, it is still highly effective and is being used to leap from one organisation to another. In this blog, I will analyse a long running phishing campaign that has compromised at least 45 different SharePoint accounts belonging to a variety of organisations over the last year. Fig. 1 - The typical phishing chain used in this campaign Fig. 2 - Various PDF documents...