Posts

Showing posts with the label Trickbot

The Continuity of Conti
Image
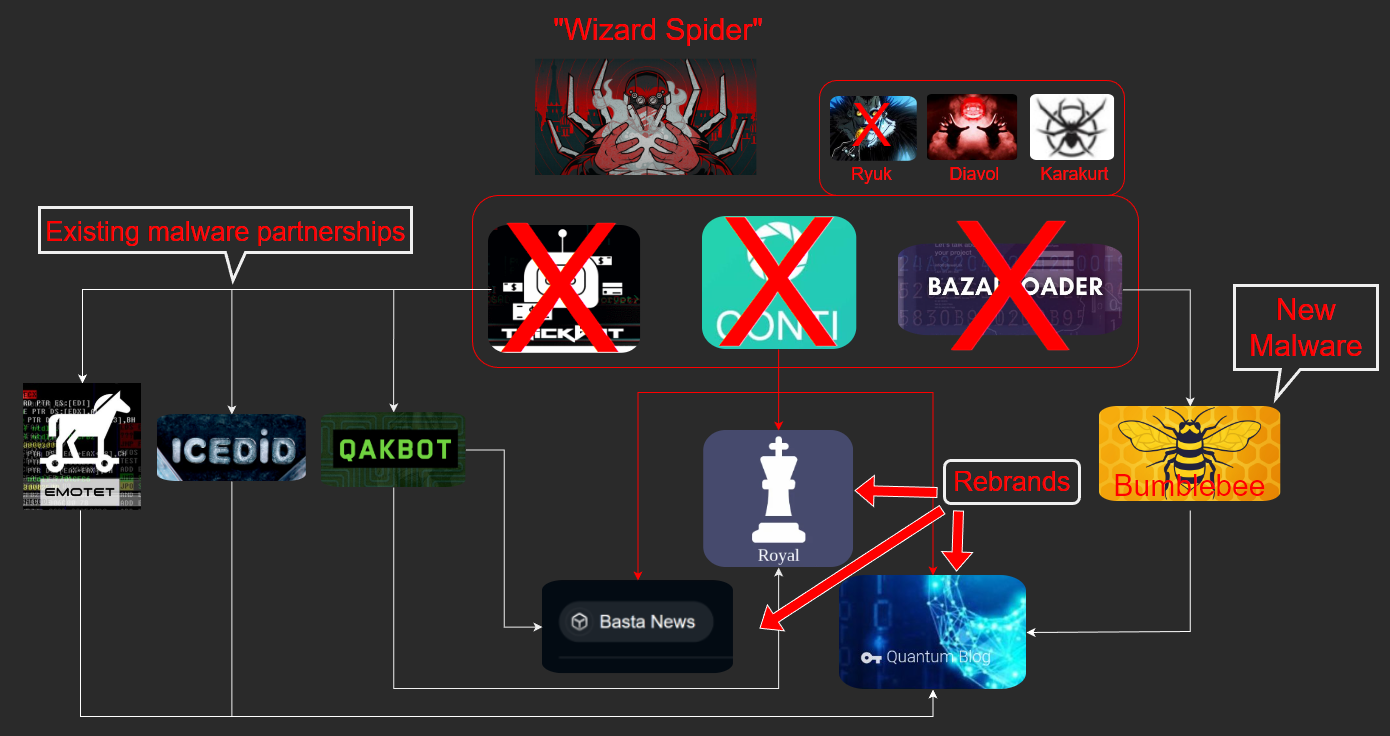
  In February 2022, following the Russian invasion of Ukraine, the operators of Conti ransomware announced their support of the Russian government. They shortly walked back their support, seemingly after rifts by members of the group. Not long after that, hundreds of thousands of messages from internal chat logs were shared publicly by two accounts on Twitter called @ContiLeaks and @TrickLeaks. This treasure trove of information revealed a wealth of insights about the inner workings of a sophisticated Russian cybercrime business linked to the Conti and Ryuk ransomware campaigns and Trickbot malware botnet , which are tracked as Wizard Spider (by CrowdStrike ), DEV-0193 (by Microsoft ), GOLD ULRICK (by Secureworks ), and  Ryuk as FIN12 (by  Mandiant ) . Following the fallout of the internal chat leaks, the Conti ransomware group carried on, seemingly business as usual. In April 2022, the Government of Costa Rica had to declare a state of emergency following a sprawling C...

Lessons from the Conti Leaks

Image
  If you wanted to learn how an organized cybercriminal operation worked, look no further than the threat group known as Conti. The recent leaks of the group's chat logs have uncovered an unprecedented wealth of information and insights into how these veteran cybercriminals organize themselves.  Cyber Threat Intelligence (CTI) vendors and independent researchers have spent weeks poring over the Conti leaked chat logs and have uncovered dozens of very significant findings.  In this blog, I didn't want to duplicate what is already known (too much). I wanted to share some of the findings that I thought were the most interesting to me. To rapidly get up to speed on the Conti Leaks, I highly recommend other researchers to read the work in the following blogs: https://www.trellix.com/en-gb/about/newsroom/stories/threat-labs/conti-leaks-examining-the-panama-papers-of-ransomware.html https://www.secureworks.com/blog/gold-ulrick-leaks-reveal-organizational-structure-and-relat...

How Do You Run A Cybercrime Gang?

Image
Cybercrime has many forms, the most common of which is theft and fraud. Aspiring cybercriminals may begin with off-the-shelf malware or phishing kits and run amateur, but profitable, campaigns. Banking Trojans were the next step up, which intercept and manipulate connections during online banking procedures for exploitation and wire fraud. Several infamous groups that graduated from these campaigns went on to form organised crime syndicates and launch 'big game hunting' ransomware campaigns. Ransomware in particular, has caused mass disruption on a national level and huge financial losses. This blog will explore three top-tier cybercrime syndicates which are tracked by the private cybersecurity industry as EvilCorp, WizardSpider, and FIN7. These threat actors are financially motivated cybercriminals whose campaigns have become a scourge to organisations and society at large. So much so, that they are closely tracked by intelligence agencies and international law enforcement. Fi...

The Lazarus Heist: Where Are They Now?

Image
  Introduction The BBC World Service has recently produced The Lazarus Heist podcast (available here ), researched and presented by Geoff White and  Jean H. Lee . This thrilling podcast dives into the intracacies of the elaborate Bangladesh Bank heist attempt to steal $1 billion. As a security researcher that actively tracks the Lazarus group and any mentions of North Korean cyber activity, I found this podcast series was extremely detailed and well researched. There are so many additional info gems that anyone who has researched North Korea will enjoy. I also highly recommend it for any threat intelligence analysts investigating North Korean cyber activity.  The Lazarus Heist podcast also made me want to revisit what I have learned about North Korean advanced persistent threat (APT) groups. In February 2020, I blogged about who the Lazarus group is and what campaigns they are known for (see here ). This was one of my first blogs and I was eager to learn more while resea...