Posts

Showing posts with the label spam emails

SharePoint Island Hopping: Phishing with compromised accounts
Image
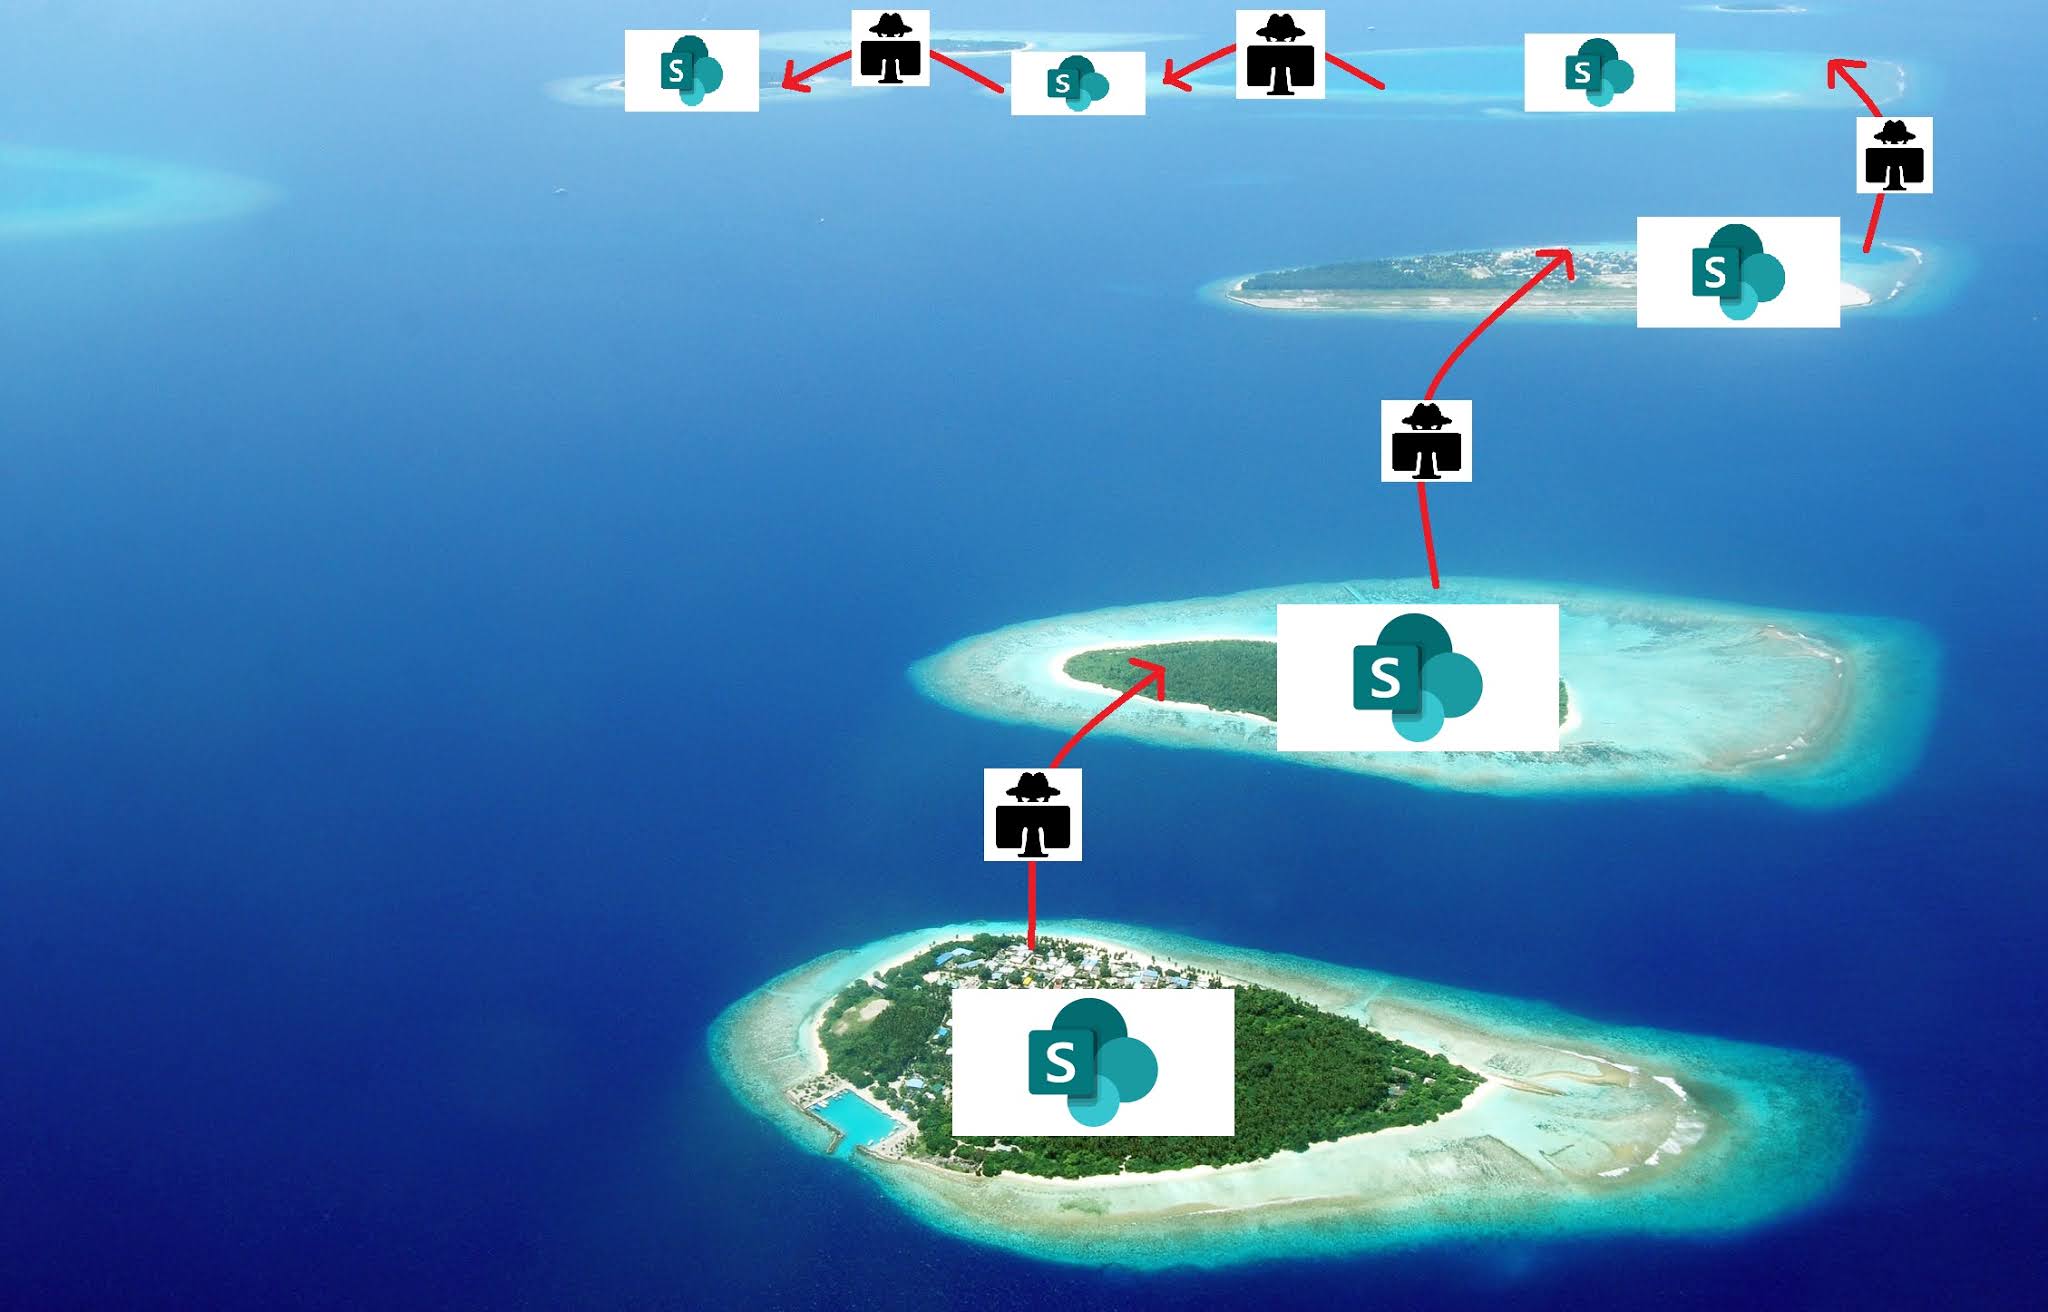
  Phishing threat actors continue to launch successful credential harvesting campaigns via compromised Office 365 accounts. One of the most common themes for these campaigns is a "shared file" notification, whereby a compromised account shares a file with a user that is hosted in the SharePoint drive. The file is usually a PDF document that contains a URL to an external site embedded in an "open document" or "view file" button. If the user clicks on it and enters their credentials they are redirected to login.microsoftonline.com. Although this is an older scam, that has been around for several years, it is still highly effective and is being used to leap from one organisation to another. In this blog, I will analyse a long running phishing campaign that has compromised at least 45 different SharePoint accounts belonging to a variety of organisations over the last year. Fig. 1 - The typical phishing chain used in this campaign Fig. 2 - Various PDF documents...

Gone Phishing

Image
This is a blog on some of the latest phishing threats that are out there and ones I have recently, personally experienced and reverse engineered. On 1 May I received this SMS text:  Just received this: (1 May) http://security[.]hsbcuk[.]confirm-securekey[.]com @HSBC_UK #phishing #smishing (I’m not with HSBC) pic.twitter.com/HU3sqBlPhz — Will | BushidoToken 👁‍🗨 (@BushidoToken) May 1, 2020 To me, it was quite clearly a phish, as I'm not with HSBC, however, someone who is may have been easily fooled. The trick the phishermen used here is via a subdomain. Average users may be able to recognise their usual bank domain and feel safe. However, the threat actors who sent this to me could use a domain like 'digitalbanking.com' (which is for sale ) and simply insert my bank's full URL as a subdomain - making it quite convincing. Plus, they can add a free digital certificate from Let's Encrypt CA to give it HTTPS and now we have a pretty convincing phish. ...