Posts

Showing posts with the label Conti

Analysis of Counter-Ransomware Activities in 2024

Image
  The scourge of ransomware continues primarily because of three main reasons: Ransomware-as-a-Service (RaaS), cryptocurrency, and safe havens. RaaS platforms enable aspiring cybercriminals to join a gang and begin launching attacks with a support system that help extract ransom payments from their victims. Cryptocurrency enables cybercriminals to receive funds from victims around the world without the option to freeze or refund them due to the immutable nature of the virtual funds. Safe havens are countries that permit cybercriminals to launch attacks without immediate fear of arrest, enabling them to earn vast fortunes through ransomware campaigns. With these three challenges in mind, law enforcement and governments have a very difficult job to do when it comes to fighting ransomware but fight it they must. In this blog we shall recall what counter-ransomware activities took place in 2024, analyse their effectiveness, and assess how the landscape shall evolve as a result. A...

Tracking Adversaries: The Qilin RaaS

Image
This blog is part of my Tracking Adversaries blog series, whereby I perform a summary analysis of a particular adversary that has caught my attention and made me feel like they deserve special attention and investigation. Qilin has been covered already by experts from Trend Micro , Secureworks , Group-IB , SentinelOne , SOCRadar , BleepingComputer , and MalwareHunterTeam . Kudos to them, because without these researchers sharing their findings with the community, we would be a lot less informed about this prominent ransomware gang. Background Active since at least May 2022, Qilin ransomware is named after the mythical Chinese creature  which you may  pronounce as "Chee-lin". The origin of this cybercriminal threat group, however, is believed to be from Russia. Like many other ransomware campaigns run by organised cybercriminal gangs, Qilin ransomware is used for domain-wide encryption of servers and workstations and its operators steal vast quantities of data. A ran...

Tracking Adversaries: Akira, another descendent of Conti

Image
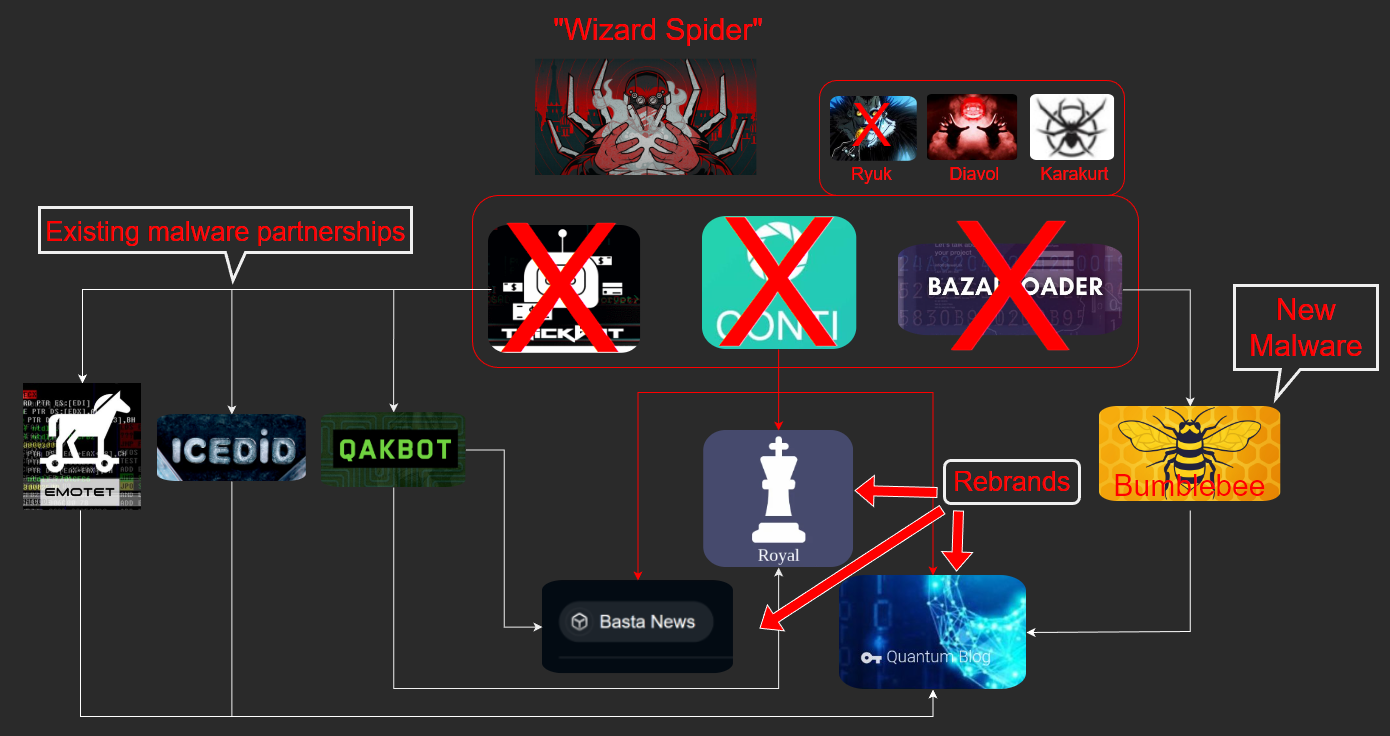
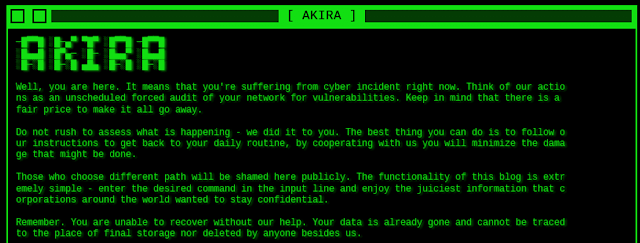
The dozens of cybercriminals that made up the Conti group continue to launch campaigns unabated. Previously in 2022, I blogged about how following the Conti Leaks , the operators of Conti  continued on via multiple rebranded ransomware campaigns, such as Royal, BlackBasta, and Quantum, among others.  Since my last two blogs on the Conti/TrickBot gang, multiple members have been officially sanctioned by the US and UK government in February 2023 and September 2023 , formally confirming attribution to Russia-based threat actors. The sanctions are a vital step in the right direction and helps the public and law makers understand what organized cybercrime looks like and the scale of the fight on our hands. In this blog, however, I wanted to explore the ransomware campaign called Akira that appeared in March 2023  and focus on how Akira is connected to Conti. Akira is a rapidly growing threat to civil society and critical infrastructure and is the ransomware group I believe r...

The Continuity of Conti

Image
  In February 2022, following the Russian invasion of Ukraine, the operators of Conti ransomware announced their support of the Russian government. They shortly walked back their support, seemingly after rifts by members of the group. Not long after that, hundreds of thousands of messages from internal chat logs were shared publicly by two accounts on Twitter called @ContiLeaks and @TrickLeaks. This treasure trove of information revealed a wealth of insights about the inner workings of a sophisticated Russian cybercrime business linked to the Conti and Ryuk ransomware campaigns and Trickbot malware botnet , which are tracked as Wizard Spider (by CrowdStrike ), DEV-0193 (by Microsoft ), GOLD ULRICK (by Secureworks ), and  Ryuk as FIN12 (by  Mandiant ) . Following the fallout of the internal chat leaks, the Conti ransomware group carried on, seemingly business as usual. In April 2022, the Government of Costa Rica had to declare a state of emergency following a sprawling C...

Lessons from the Conti Leaks

Image
  If you wanted to learn how an organized cybercriminal operation worked, look no further than the threat group known as Conti. The recent leaks of the group's chat logs have uncovered an unprecedented wealth of information and insights into how these veteran cybercriminals organize themselves.  Cyber Threat Intelligence (CTI) vendors and independent researchers have spent weeks poring over the Conti leaked chat logs and have uncovered dozens of very significant findings.  In this blog, I didn't want to duplicate what is already known (too much). I wanted to share some of the findings that I thought were the most interesting to me. To rapidly get up to speed on the Conti Leaks, I highly recommend other researchers to read the work in the following blogs: https://www.trellix.com/en-gb/about/newsroom/stories/threat-labs/conti-leaks-examining-the-panama-papers-of-ransomware.html https://www.secureworks.com/blog/gold-ulrick-leaks-reveal-organizational-structure-and-relat...