Posts

Showing posts with the label Emotet

The Continuity of Conti
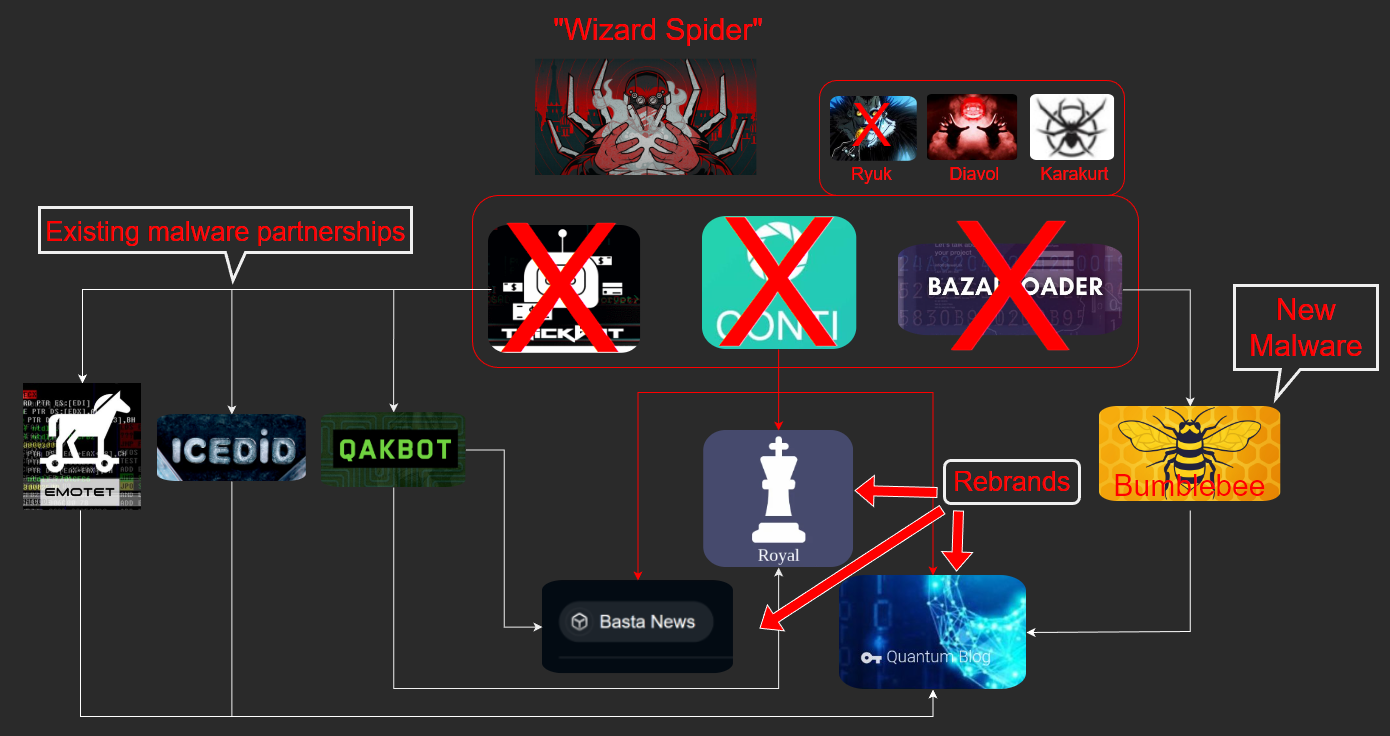
Image
  In February 2022, following the Russian invasion of Ukraine, the operators of Conti ransomware announced their support of the Russian government. They shortly walked back their support, seemingly after rifts by members of the group. Not long after that, hundreds of thousands of messages from internal chat logs were shared publicly by two accounts on Twitter called @ContiLeaks and @TrickLeaks. This treasure trove of information revealed a wealth of insights about the inner workings of a sophisticated Russian cybercrime business linked to the Conti and Ryuk ransomware campaigns and Trickbot malware botnet , which are tracked as Wizard Spider (by CrowdStrike ), DEV-0193 (by Microsoft ), GOLD ULRICK (by Secureworks ), and  Ryuk as FIN12 (by  Mandiant ) . Following the fallout of the internal chat leaks, the Conti ransomware group carried on, seemingly business as usual. In April 2022, the Government of Costa Rica had to declare a state of emergency following a sprawling C...

Lessons from the Conti Leaks

Image
  If you wanted to learn how an organized cybercriminal operation worked, look no further than the threat group known as Conti. The recent leaks of the group's chat logs have uncovered an unprecedented wealth of information and insights into how these veteran cybercriminals organize themselves.  Cyber Threat Intelligence (CTI) vendors and independent researchers have spent weeks poring over the Conti leaked chat logs and have uncovered dozens of very significant findings.  In this blog, I didn't want to duplicate what is already known (too much). I wanted to share some of the findings that I thought were the most interesting to me. To rapidly get up to speed on the Conti Leaks, I highly recommend other researchers to read the work in the following blogs: https://www.trellix.com/en-gb/about/newsroom/stories/threat-labs/conti-leaks-examining-the-panama-papers-of-ransomware.html https://www.secureworks.com/blog/gold-ulrick-leaks-reveal-organizational-structure-and-relat...

Emotet Returns

Image
#Emotet botnet Incoming! pic.twitter.com/HxPYNAhxhM — Will | BushidoToken 👁‍🗨 (@BushidoToken) July 17, 2020 The infamous Emotet botnet has returned. In February 2020, the Emotet botnet, largely made up of compromised WordPress servers, ceased to send spam emails. This period of inactivity has now ended with threat intelligence sources now observing an even large number of URLs and C&C servers than before. Emotet botnet activity resumed around 15-17 July 2020. That was when the first confirmed emails leading to Emotet infection were first observed. Emotet aims to not only steal information, but also send spam emails using stolen credentials from infected terminals and attempts to spread the malware further. The typical Emotet infection chain: Current Emotet documents with embedded macros (as of July 2020): Media coverage of Emotet since its return: MSTIC: https://twitter.com/MsftSecIntel/status/1284206817136926720 Malwarebytes: https://blog.malwarebytes.com/trojans/2020/07/long-d...

The most dangerous malware in the world: Emotet

Image
To earn the title ‘most dangerous malware in the world’ is not a simple task, due to the abundance of cybercriminals and nation state threat actors who are continuously working towards that goal too. However, it is not something you can wave proudly as it requires anonymity and the capability to operate with impunity from locale in which you reside, or without that country's knowledge (very unlikely). The usual suspects on the world stage of malware development can include Russia, China, North Korea, and Iran. But other groups pop up here and there such as, the US and UK for example, or even Israel, which like to do it with discretion - unlike their counterparts. At this moment in time, Emotet is widely believed by the security industry to be the most dangerous in the world. First identified in 2014, this Trojan downloader has gripped the security community since its return in September 2019, after a several month long Summer vacation . Emotet has a complex infection ...