Posts

Showing posts with the label qakbot

Lessons from the BlackBasta Ransomware Attack on Capita

Image
Introduction When a company that manages data for millions of UK citizens falls victim to ransomware, the whole industry should pay attention to it. On 15 October 2025, the UK Information Commissioner’s Office (ICO) published a detailed 136 page report about the Capita breach.  The aim of this blog is to extract actionable cybersecurity lessons from the ICO’s findings as well as open source reports surrounding the breach from a cyber threat intelligence (CTI) analyst’s perspective to help SOC and CERT teams, and CISOs understand what happened and how to avoid the mistakes made by others. BLUF Incident Impact Summary: Capita was attacked by BlackBasta ransomware in March 2023 Over six million individual’s records were exfiltrated from Capita’s systems A £14 million fine was issued to Capita by the ICO Capita said in May 2023, the incident cost up to £20 million to recover Important context about Capita The Capita Group is a business process outsourcing (BPO) and professional servic...
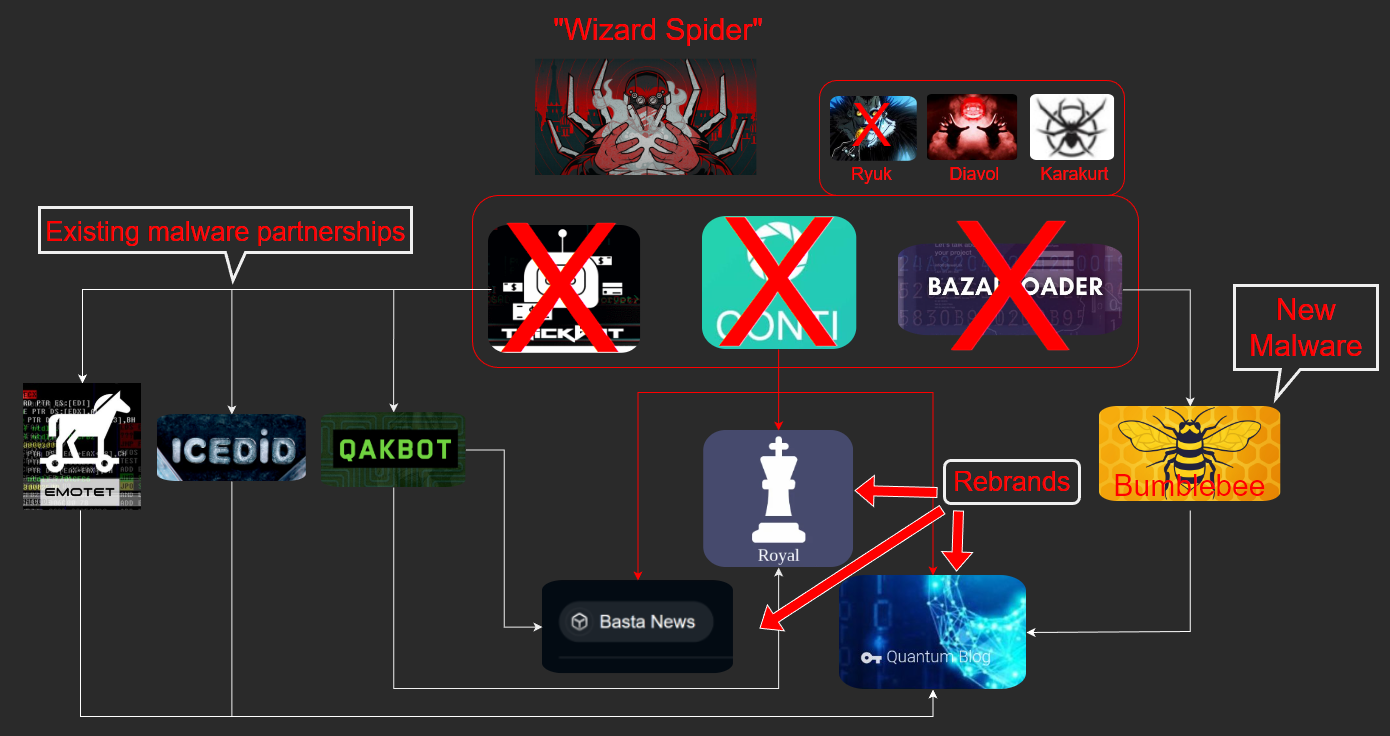
The Continuity of Conti

Image
  In February 2022, following the Russian invasion of Ukraine, the operators of Conti ransomware announced their support of the Russian government. They shortly walked back their support, seemingly after rifts by members of the group. Not long after that, hundreds of thousands of messages from internal chat logs were shared publicly by two accounts on Twitter called @ContiLeaks and @TrickLeaks. This treasure trove of information revealed a wealth of insights about the inner workings of a sophisticated Russian cybercrime business linked to the Conti and Ryuk ransomware campaigns and Trickbot malware botnet , which are tracked as Wizard Spider (by CrowdStrike ), DEV-0193 (by Microsoft ), GOLD ULRICK (by Secureworks ), and  Ryuk as FIN12 (by  Mandiant ) . Following the fallout of the internal chat leaks, the Conti ransomware group carried on, seemingly business as usual. In April 2022, the Government of Costa Rica had to declare a state of emergency following a sprawling C...

Gathering Intelligence on the Qakbot banking Trojan

Image
Background:  The Qakbot banking Trojan is one of the top-tier malware families on the current threat landscape. It is distributed in mass spam campaigns, steals confidential information, and has also provided access to ransomware operators. Preventing and detecting this threat has become a priority for many organisations as a successful infection can lead to a costly cyber incident. In this blog, I aim to share more information on this malware, provided by open sources, and highlight the intelligence gathering process it takes to combat this threat. Qakbot (also known as Quakbot or Qbot) has been around since 2008. It has targeted the customers of various financial institutions worldwide. While Qbot's targeting has mostly remained the same - with the aim of stealing bank details and enabling wire fraud - its propagation methods have changed across various campaigns. Despite its age, Qakbot still remains a significant threat with established connections in the organised cybercr...